NVIDIA Sentry puts agent containment on BlueField-4
NVIDIA says Sentry can contain agents within milliseconds from a hardware-isolated domain on BlueField-4 DPUs, independent of host software at runtime.
| NVIDIA Sentry | |
|---|---|
| hardware | BlueField-4 DPUs |
| runtime | DOCA |
| domain | hardware-isolated trust domain |
| policy engine | Open Policy Agent rules |
| memory introspection | DOCA Argus |
| containment | within milliseconds |
| records | attested telemetry and tamper-evident records |
4 is the number in BlueField-4, the DPU named for Sentry's hardware-isolated enforcement. That number does not prove a published price, a ship date, or a measured containment latency.
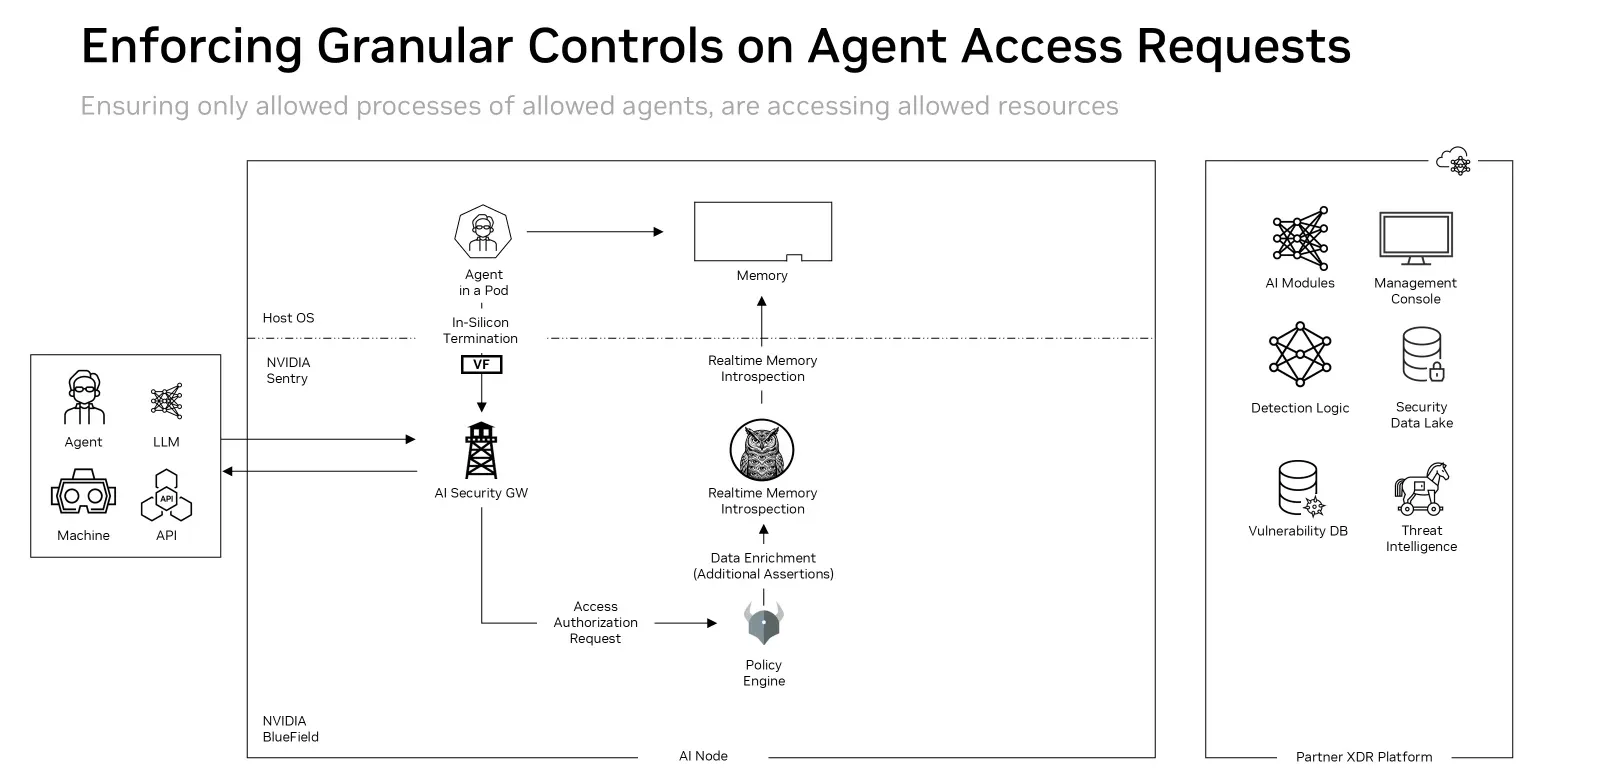
The document constrains the host, not the buyer. Sentry sits outside the agent and host software, so the platform vendor must route the model path through BlueField-4 to make the stop point real. DOCA Tower terminates TLS and checks requests against Open Policy Agent rules, while DOCA Argus reads the agent's memory state. For a buyer, the useful change is that containment is claimed at the network boundary, not inside the agent's own runtime.
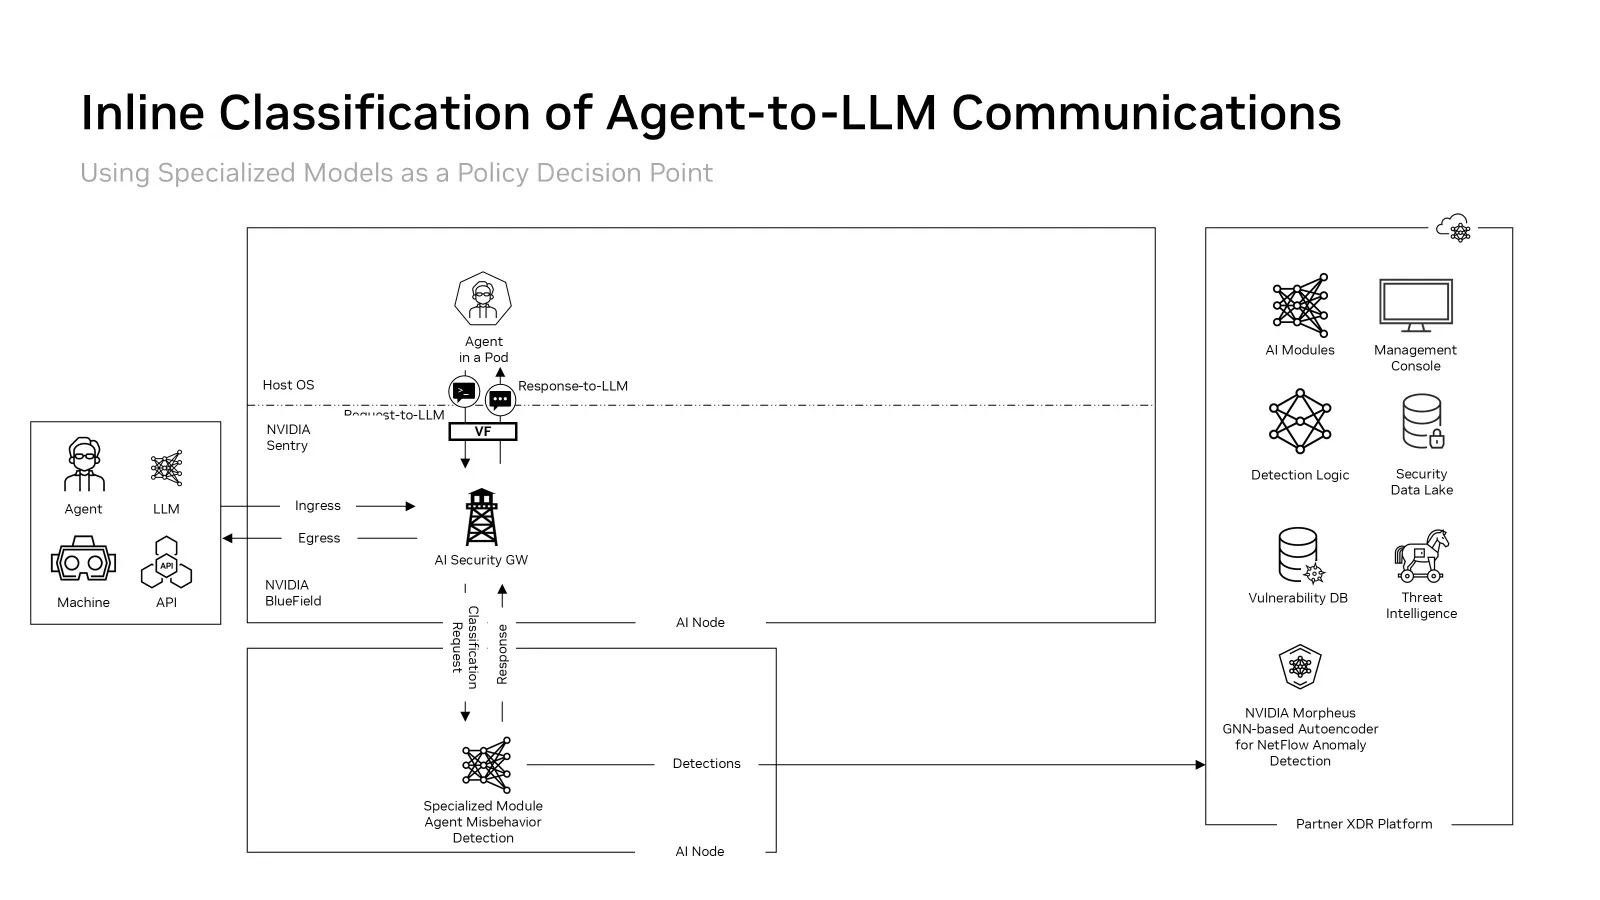
No exact millisecond figure, power draw, price, availability date, or breakout benchmark appears in the filing. The vendor also leaves the enterprise security integrations unnamed, so the buyer cannot price the stack yet or verify it independently.
The host is the constrained party, because Sentry's enforcement lives outside the agent and host software. The buyer gains a claimed network-boundary stop point, but no price or measured latency yet.
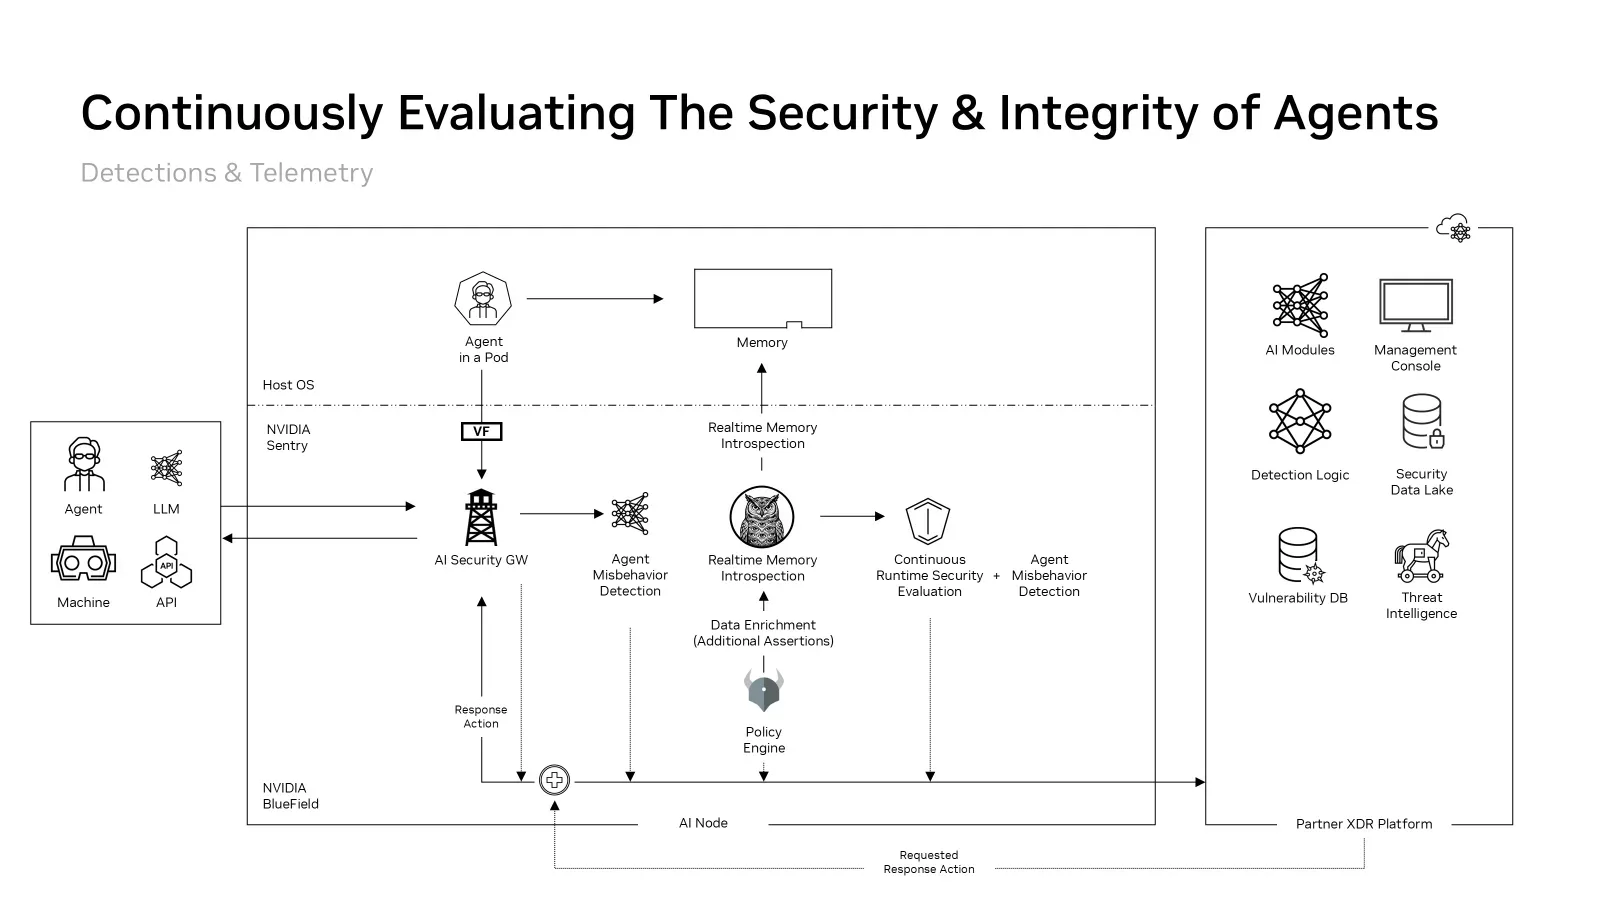
No exact containment latency, price, availability date, power draw, or breakout benchmark is given.
Sentry moves policy checks to a DPU domain: DOCA Tower terminates TLS and applies OPA rules, while DOCA Argus inspects memory. That gives the platform vendor a host-independent containment point, but the document still lacks price, power, and exact latency.
After developer.nvidia.com. We did not report this. The pictures, if any, are theirs.